Introducing PTaaS+: Decreasing Your Organization’s Time to Remediation
The PTaaS+ features listed within this blog post are now offered with any NetSPI service that leverages PTaaS. This excludes ticketing integrations, which are available for an additional cost. Contact us to learn more.
NetSPI is focused on creating the next generation of security testing. Our Penetration Testing as a Service (PTaaS) delivers higher quality vulnerabilities, in less time than any other provider and we are now expanding these benefits into your remediation lifecycle.
This month we’re expanding your options with our PTaaS+ plan, which focuses on vulnerability management and remediation. With our base PTaaS plan, we deliver vulnerabilities the same day they are found, now with PTaaS+ you and your team are empowered to act upon and begin remediating them immediately, decreasing your time-to-remediation by up to 1 month for high severity issues. A couple of key features contribute to this new functionality:
Ticketing Integrations
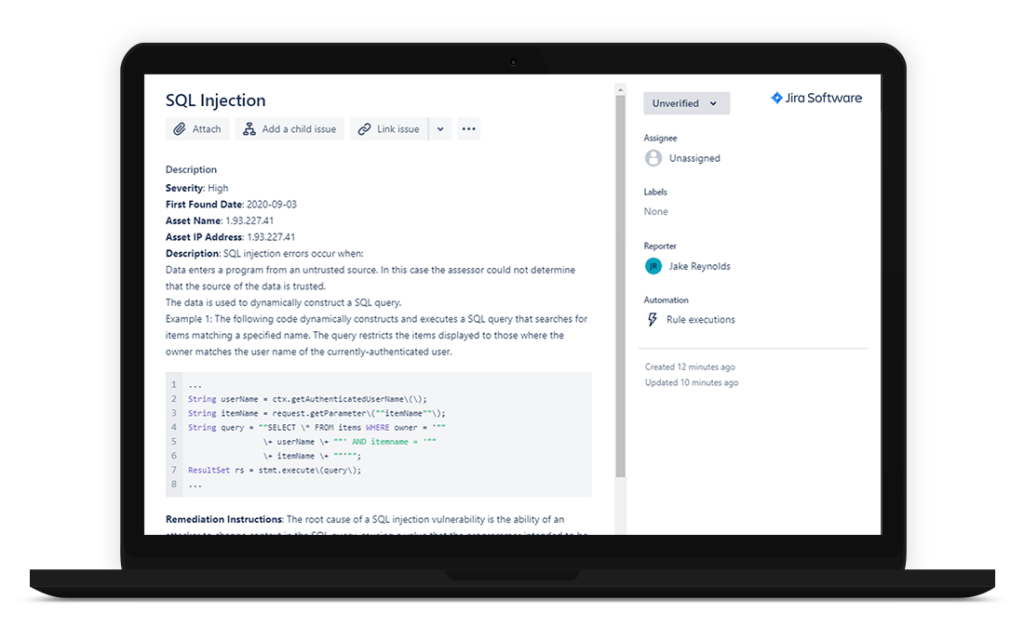
On average, we report over 50 vulnerabilities on a regular web application test, that number jumps above 700 when we perform external network testing. When receiving so many vulnerabilities, making sense of it all can be a full-time job before you even get to remediating them. With PTaaS+, we offer free integration with Jira or Service Now to easily get the vulnerabilities into your tools and into the remediator’s hands on day zero.
Remediation Assignments & SLAs
After receiving a large number of vulnerabilities, the first step is assigning a due date for remediation based on vulnerability severity. PTaaS+ allows each severity to be assigned a timeframe in which it must be remediated from the delivery date. NetSPI’s standard recommendation is:
- Critical – 30 days
- High – 60 days
- Medium – 90 days
- Low – 365 days
However, these can be customized to fit your organization’s policies. Additionally, with PTaaS+, you can assign vulnerabilities to specific users, letting you track and delegate vulnerabilities throughout the remediation lifecycle.
Vulnerability Customization
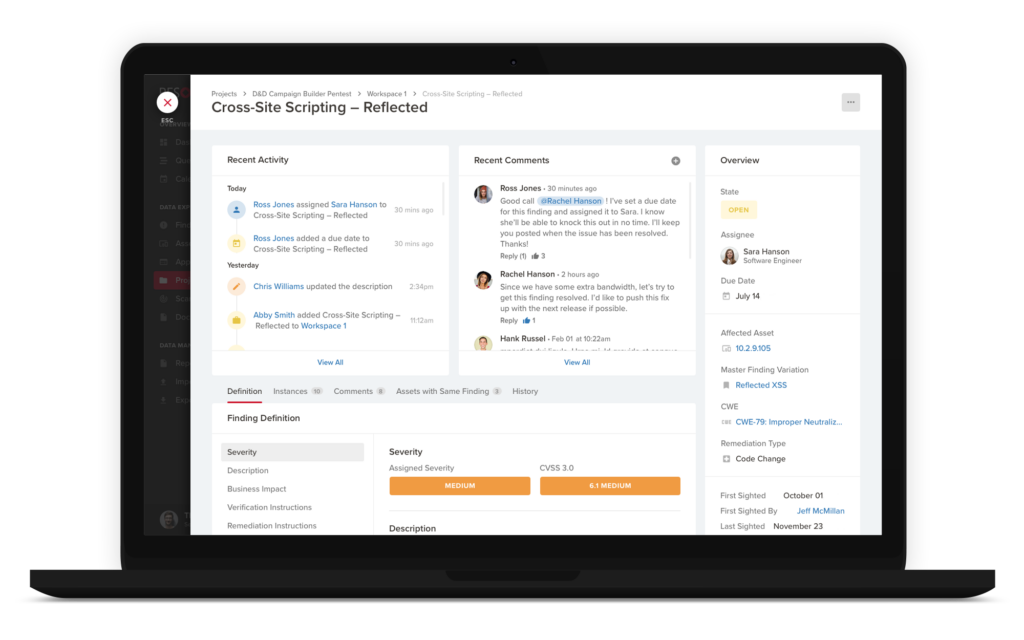
After delivering vulnerabilities, one common point of discussion is NetSPI’s severity rating vs. an organization’s internal vulnerability rating. Every organization rates vulnerabilities differently and to help with that, PTaaS+ allows you to provide an assigned severity to all vulnerabilities, from which your remediation due dates can be calculated. Both NetSPI’s and your severities will be maintained for auditing and future reporting.
Data Analytics
After you have a handle on your remediation processes, you can start looking for trends to ensure fewer vulnerabilities next year. PTaaS+ grants you access to NetSPI’s Data Lab which allows you to analyze and trend vulnerabilities across all your assessments with NetSPI. Popular data lab queries include:
- Riskiest asset in your environment
- Most common vulnerabilities across your company
- Top OWASP categories
The PTaaS+ features listed within this blog post are now offered with any NetSPI service that leverages PTaaS. This excludes ticketing integrations, which are available for an additional cost. Contact us to learn more.
Explore More Blog Posts
Authorization Differential Testing in Salesforce
NetSPI Salesforce expert Aussan explores how holding identity steady across UI API, GraphQL, and custom @AuraEnabled Apex methods reveals hidden authorization gaps.
PHP2Shell Unauthenticated RCE on PHP: CVE-2026-109618 & CVE-2026-109619
The PHP project has disclosed two critical vulnerabilities, CVE-2026-109618 and CVE-2026-109619, affecting all PHP installations that serve web requests. Both vulnerabilities carry a CVSS 4.0 score of 9.2 (Critical).
Introducing the NetSPI Platform MCP
Discover how the new NetSPI Platform Model Context Protocol (MCP) integration gives you a live view of vulnerabilities in your environment and the speed of remediation needed to counter fast-paced attackers.