Podcast
Agent of Influence
EPISODE 077 — What Security Leaders Do for Fun
From Spartan races to culinary arts, discover the hobbies and passions that keep CISOs balanced and inspired in this behind-the-scenes edition of Agent of Influence.

EPISODE 076 — Translating Security for Your C-Suite
Is cybersecurity a roadblock or growth enabler? Dave Edminster at EVOTEK shares how to reframe security as ROI-driven, turning invisible success into business value.
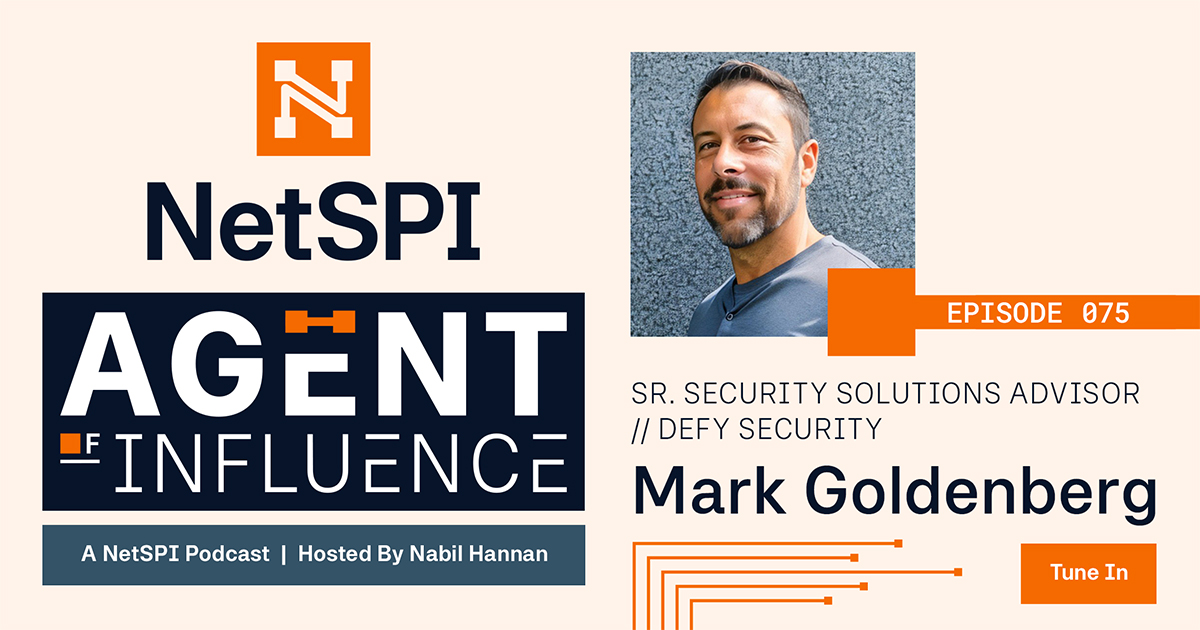
EPISODE 075 — Why “Scan, Find, Patch” Is No Longer Enough
The traditional "scan, find, patch" method is falling short against today’s threat landscape. In this episode, Mark Goldenberg, Sr. Security Solutions Architect at Defy Security, outlines a modern approach to vulnerability management.
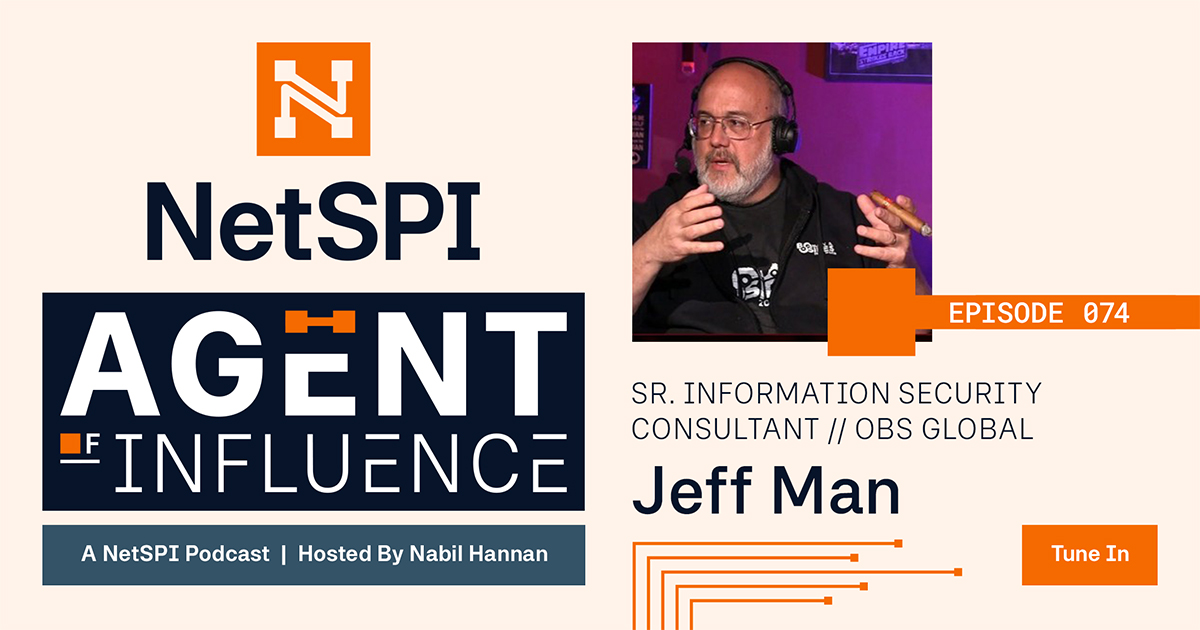
EPISODE 074 – Step into a Cybersecurity Time Machine
On Agent of Influence, Nabil Hannan and Jeff Man discuss industry fundamentals, the cryptologic cipher wheel, and empowering the next generation of cybersecurity professionals.
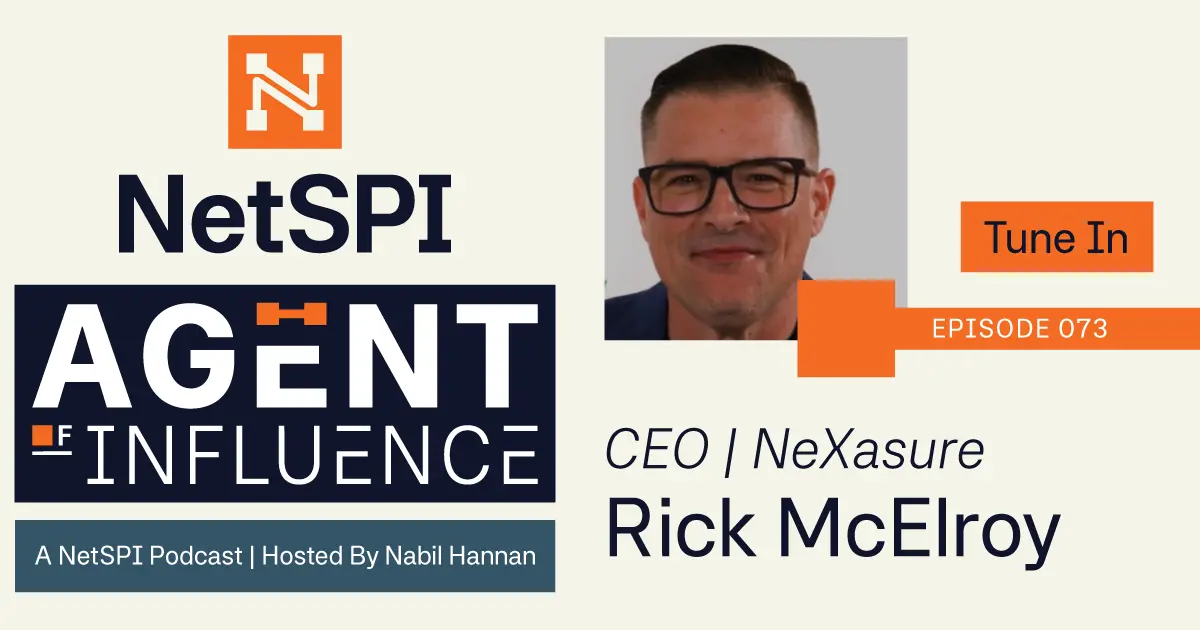
EPISODE 073 – Chief Persuasion Officer: The New CISO Mindset
Explore the evolving CISO role, AI in cybersecurity, career advice, and proactive security with Rick McElroy on the Agent of Influence podcast.
EPISODE 072 – Cybersecurity Lessons on the Path to Private Equity
Explore how private equity and cybersecurity intersect with Paul Harrigan of KKR. Learn strategies for managing risks, M&A diligence, and aligning security with growth.

EPISODE 071 – The Future of HubSpot is Passwordless
Learn how HubSpot’s CISO Alyssa Robinson breaks down passwordless authentication, innovative security strategies, and the art of balancing usability with protection.
EPISODE 070 – Advancing Exposure Management
Hear from Jorge Orchilles, Senior Director at Verizon, on the shift from traditional vulnerability management to modern exposure management and the critical role proactive security plays in staying ahead of threats.
EPISODE 069 – Does Open-Source AI Create a False Sense of Security?
Listen to Suryaprakash Nalluri discuss challenges with open-source software and the critical role of DevSecOps in modern development.

EPISODE 068 – Bridging the Cybersecurity Divide
Watch the latest Agent of Influence episode with Robert Wagner, Advisory CISO and Managing Director at NetSPI, about prioritizing security efforts for small and medium-size businesses.
EPISODE 067 – Security in Sync: Aligning Enterprise and Product Teams
Tune in to Agent of Influence with Nancy Brainerd from Medtronic to explore aligning enterprise and product security for unified cybersecurity.
EPISODE 066 – Digital Trust in the Age of AI
Hear from Aaron Shilts, CEO of NetSPI, as he explores NetSPI’s journey, how pentesting has evolved, and cyber predictions for 2025.

EPISODE 065 – New Year, New Role: 3 Key Strategies for Cyber Leaders
Join Bindi Davé, Deputy CISO at DigiCert, as she shares the Golden Triangle approach to asset discovery, risk, and building cybersecurity culture.
EPISODE 064 – The (not so) Secret Skills for Success in Cyber
Catch Robert Wood on Agent of Influence discussing third-party risk management and balancing technical and soft skills in cybersecurity.
EPISODE 063 – API Security for Everyone
Listen to Agent of Influence with Buchi Reddy of Levo.ai to dive deep into proactive API security measures and how to simplify API inventory.
EPISODE 062 – Let’s Talk Automated Red Teaming
Watch the latest Agent of Influence episode with Ryan Hays from Citi about the buzzwords, “automated red teaming”, and how to foster effective red and blue team collaboration.

EPISODE 061 – Leveraging IT Hygiene to Build a Culture of Security
Gain tactical insights on third-party risk, IT hygiene, security culture, and gender equality in cybersecurity with Nabil Hannan and Dawn Armstrong.

EPISODE 060 – Sharing a Blueprint for Cybersecurity Leadership
Listen to Tunde Oni-Daniel’s journey from cybersecurity technologist to leader and hear how to lead with purpose while building a top-tier team.

EPISODE 059 – Making Cybersecurity Accessible for All
Join Agent of Influence as Mandy Haeburn-Little discusses expanding security services in the UK and her work to attract diverse talent to cyber.
EPISODE 058 – Staying Mindful throughout Data Breaches at Any Program Maturity Level
Hear from Lee Vorthman, Chief Security Officer at Oracle, on the stages of security program maturity and how to address a data breach at any level.
EPISODE 057 – Dare to Leap: Conquering the Unknown in Cloud Security
Meet Zinet Kemal, a remarkable individual who embarked on a transformative journey from a legal career in Ethiopia to a role in cybersecurity in the United States.
EPISODE 056 – Leading with FUN Instead of FUD
Tim Derrickson joins the Agent of Influence podcast to share a new approach to FUD and explore the partnership between MSPs and pentesting providers.
EPISODE 055 – Teaching Next Gen Cybersecurity Leaders
High school cybersecurity teacher Neil Plotnick joins Agent of Influence host Nabil to talk about teaching the next wave of cybersecurity leaders.

EPISODE 054 – Secure Your Products, Secure Your Business: Insights from Envestnet’s Derek Fisher
Join Envestnet’s Derek Fisher for a deep dive into product security, learn how it differs from application security and DevSecOps, and gain other valuable insights on budgeting, communications, and risk management.

EPISODE 053 – How to Balance Cybersecurity and Compliance
Marc Rubbinaccio, Senior Compliance Manager at Secureframe, explores important cybersecurity compliance frameworks, proactive tips for staying ahead of the regulatory landscape, and the relationship between GRC and pentesting.

EPISODE 052 – High Stakes Security: Wynn Resorts CISO Covers Identity and Access Management and the Misrepresentation of Modern Hackers
David Tyburski of Wynn Resorts discusses unique cybersecurity challenges in the hospitality industry and key learnings from his experience building a comprehensive identity and access management program.
EPISODE 051 – Phil Morris – On Leveraging Organizational Psychology to Reimagine Healthcare Cybersecurity
Phil Morris at Altera Digital Health tackles the complexity in healthcare by discussing best practices in application security, risk management, ransomware, and more.
EPISODE 050 – Prepare for PCI DSS 4.0 Changes with Raymond James’ Sr. Analyst of IT Security
Heather Hirschey, Senior Analyst of IT Security at Raymond James, discusses upcoming PCI DSS 4.0 changes, vulnerability management, and resources for getting started in cybersecurity.
EPISODE 049 – Exploring Edge Data Center Security Challenges, Trends, and More
Todd Cushing, President at 1623 Farnam, discusses the importance of edge data centers plus security challenges and prevalent trends in the space.
EPISODE 048 – An Untraditional Approach to DevSecOps & The Future of Application Security Testing
Larry Maccherone, DevSecOps Transformation Architect at Contrast Security, explores the untraditional definition of DevSecOps, appsec testing tools, and the future of application security testing.
EPISODE 047 – Enabling Business Growth Through Data and Collaboration
Join Samir Sherif, CISO at Imperva, for a discussion on relationship building and networking and how to leverage risk and resiliency data to enable business growth.
EPISODE 046 – Zero Trust Misconceptions
Join Rob LaMagna-Reiter, CISO at Hudl, for a deep dive into zero trust, advice for building a cybersecurity program, and using cybersecurity data to showcase ROI.
EPISODE 045 – The Unique Challenges of Healthcare Cybersecurity
Cecil Pineda, SVP/CISO at R1 RCM, discusses prominent healthcare security concerns, impactful metrics to showcase ROI, the power of storytelling, community building, and more.
EPISODE 044 – Logistics Industry Leader Discusses How to Cultivate a Relationship Between Business and Cybersecurity
Justin Hall, CEO at PRIMO and Executive in Residence at 8VC, discusses prioritizing security in the global supply chain, third-party risk management, the true business impact of a cybersecurity breach, actionable advice for legacy players in the logistics industry, and more.
EPISODE 043 – Getting Started as a Security Leader, Addressing the Talent Shortage, and Securing the Critical Infrastructure
Jessica Nemmers, Chief Security Officer at Elevate, discusses the cybersecurity talent gap, women in cybersecurity, how to build a solid security program foundation, critical infrastructure vulnerabilities, and more.
EPISODE 042 – Deception Technology, Identity Detection and Response, Cloud Security, and More
Attivo Networks’ Carolyn Crandall, a top female leader in cybersecurity, delves into deception technology, identity detection and response, cloud security and adoption, endpoint security, and more.
EPISODE 041 – What is Secure Access Service Edge (SASE) and How Has it Evolved in Recent Years?
Netskope's Jason Clark and James Robinson discuss secure access service edge (SASE), the accelerated growth of cloud adoption, zero trust network access, and more.
EPISODE 040 – The State of Authentication and Best Practices for Digital Certificate Management
Jason shares his thoughts on the state of authentication, best practices for managing digital certificates, the role of AI and machine learning in threat detection, and more.

EPISODE 039 – Contextual AppSec Testing, Open Source Security, Log4j, and More
Idan discusses contextual application security testing, open source security, dependency confusion, Log4j, and more.

EPISODE 038 – A Deep Dive into SaaS Security Posture Management (SSPM)
Maor discusses SaaS security posture management (SSPM), the challenges of securing a SaaS stack, the Adaptive Shield origin story, the concept of secure by default, and more.

EPISODE 037 – A Day in the Life of a NetSPI Penetration Tester
Austin and Marissa discuss penetration testing, NetSPI University, computer science curricula, cybersecurity career misconceptions, characteristics of a successful pentester, and more.

EPISODE 036 – “Cybersecurity is Everyone’s Business” | How Can We Make Cybersecurity More Mainstream?
Dave discusses cybersecurity readiness factors, the CISO function, today’s cybersecurity curriculum, rewarding failure, how to make security more mainstream, and more.
EPISODE 035 – Middle School Teacher Turned CISO Talks Reverse Engineering, Asset Management, and More
Seth discusses his unconventional career path, the CISO role, reverse engineering, cyberattack trends in the insurance space, the most effective security activities, and more.
EPISODE 034 – The Future of Penetration Testing is Not Check-the-Box | Get to Know NetSPI’s New CTO
Travis discusses his new CTO role at NetSPI, the value of tech-enabled services, the future of pentesting, virtual CISOs, the state of security education, and what’s “next next” in cybersecurity technology innovation.
EPISODE 033 – The Evolution of Incident Response, Lessons Learned from Chinese-Based Tech Companies, Mental Health, and More
Doug discusses the evolution of incident response, asset inventory, his work with DJI Drones and TikTok, mental health, neurodiversity, and more.

EPISODE 032 – “Shift Left, But Not Too Left”: A Conversation on AppSec and Development Trends
Maty discusses application security and development trends, open-source and API security challenges, the concept of shift left, the future of IAST, static analysis best practices, and more.
EPISODE 031 – What’s Keeping Security Leaders Up at Night? DDoS, Ransomware, 5G, and Security Employment
Kaz discusses creative problem solving, DDoS attack trends, how 5G and the hybrid workforce are shifting attack patterns, ransomware payments, cybersecurity staffing, smart home security, and more.
EPISODE 030 – Communicating Cybersecurity ROI, AppSec Frameworks, AI and ML Security, and More
Diana discusses tips for communicating cybersecurity ROI to leadership, the top frameworks and processes for application security, DevSecOps, how to safely leverage machine learning and artificial intelligence, inclusivity in cybersecurity, and more.
EPISODE 029 – Application Security and Penetration Testing Insights from a Utilities Sector CISO
Manish discusses utility sector cybersecurity challenges, consultancy versus internal cybersecurity careers, the future of penetration testing, threat modeling success stories, advice on how to build an application security champions program, and more.

EPISODE 028 – Is Data Science the Key to a Mature Security Program?
Jim shares insights on how to define and encourage innovation, building a mature security program using data science, why risk frameworks alone are not enough, security past versus security present, and more.
EPISODE 027 – The Secret Service, Modern Bank Heists, Defensive Security, and More
Tom discusses financial sector security, his latest research on Modern Bank Heists, SolarWinds, tips for effective cyber security defense, cloud security, insights from the Obama administration cyber security commission, and more.
EPISODE 026 – The Evolution of Risk Management and the Chief Risk Officer
Jeff discusses the evolution of risk management, how to succeed as an advisory board member, PCI compliance, the convergence of cyber and physical security, and more.
EPISODE 025 – How Well Do You Know Your Breach Preparedness, Incident Response, and Regulatory Obligations?
Matt discusses today’s biggest cyber security threats and defines privacy vs. security incidents. He also shares advice for breach preparedness, understanding privacy regulations, disaster recovery, and more.
EPISODE 024 – Startup Security, Threat Modeling, Pre-Social Engineering, and More
Hadas highlights insights from her career as a startup security leader, the importance of threat modeling, how “pre-social engineering” works, and more.

EPISODE 023 – From Wealth Management to Vulnerability Management – Insights Gained from a Unique Career Path
David shares his insights on leadership, mentorship, and community involvement from both his wealth management and cyber security industry experience.
EPISODE 022 – Culture Eats Strategy for Breakfast: Acquisition and InfoSec Insights from NetSPI’s New CTO
Brady shares the importance of offensive security, how he took his hobby building malware to the next level, acquisition advice, and more.
EPISODE 021 – Comfort is the Enemy: Leadership Advice from a Top Woman in Cyber Security
Jadee discusses key learnings from the 2013 Target breach, advice for security leaders getting too comfortable, why application security needs to shift left, and more.
EPISODE 020 – What Makes a Successful Technologist, A Day in the Life of a Security Firm CISO, and Lessons from an Effective Phishing Engagement
Roshan discusses the challenges and opportunities of being a CISO at a security firm, business lessons learned from a phishing engagement, how to reduce security friction, and more.

EPISODE 019 – Tech Resiliency Amid COVID-19 and Criteria for an Investment-Worthy Company
Gus discusses the resiliency of the technology industry amid COVID-19 and what makes a company worthy of an investment.
EPISODE 018 – Wireless Security Challenges, SMS Evolution, 3G Flaws, and 5G Implications
Guevara talks about unique security challenges related to wireless systems, the evolution of SMS, flaws in how 3G was implemented, and how the world may change once 5G is broadly available.
EPISODE 017 – A Peek into the Development of India’s First Computer Crimes Unit and IT Act of 2000
Vikram talks about building one of the first computer crimes units in India and how his security background has informed his business ventures.
EPISODE 016 – Mentorships, M&As and IPOs from a Security Perspective, and Advising Early-Stage Start-ups
Ty talks about mentorship relationships, M&As and IPOs from a security perspective, and advising early-stage start-ups.
EPISODE 015 – How to Modernize Your AppSec Program from Jeff Williams, a Key Contributor to the OWASP Top 10
Why Jeff developed IAST and its benefits, and the power of instrumentation to automate some components of your vulnerability testing.
EPISODE 014 – Dark Reading’s Executive Editor Shares Her Perspective on Cyber Security
How one of the top 10 cyber security journalists in the country got into the industry, her perspective, and some of her favorite topics she’s covered.

EPISODE 013 – Building Security into the SDLC: An IAST Evangelist’s Perspective
How IAST is revolutionizing the application security space, the future of agent-based technology, and why it’s so hard to train developers to code securely.
EPISODE 012 – Cyber Security is Boring: Doing the Hard Work to Provide a Safe and Secure Workplace
Kristin shares about unique areas of focus in the biotech industry, creating a culture of education around cyber security, and getting past the shame of falling victim to a scam.
EPISODE 011 – LogMeIn’s CISO Shares Insight into Growing a Security Program – and Common Challenges
Starting and growing a security program and team is a challenge – but start from the beginning, and hear from LogMeIn’s CISO about taking on common challenges.

EPISODE 010 – The Payment Card Industry: At the Crossroads of Convenience and Security
Convenience is driving innovation in the payment card industry and raising new challenges around privacy, security, and points of sale.
EPISODE 009 – One InfoSec Veteran’s Journey to Cyber Security & The Biggest Challenges Faced by CISOs Today
Hear what one IT and InfoSec veteran says is the biggest challenge facing CISOs today – and get advice for tackling these challenges and starting in a new senior-level cyber security role.

EPISODE 008 – Three Keys to Application Security – and the Criticality of Cross-Functional Relationships
Get advice from a 40-year information security veteran about three key components to ensuring application security – especially building relationships and getting buy-in across the organization.
EPISODE 007 – Building Secure Software and a Peek into the Cyber Security of the Brazilian Elections
Hear from an internationally recognized information security leader about factors that influence the development of secure software and get a peek into cybersecurity of the Brazilian elections.
EPISODE 006 – The Evolving History of Cyber Security – From Mainframes to the Cloud
Insight from a 25-year security veteran helping organizations adopt cloud security, an avid traveler, and insights on exploring eastern philosophy.
EPISODE 005 – Why Your Company Should Prioritize Data Privacy – and Implications If You Fail To Do So
Learn from a data privacy expert about how to protect your own personal data and set your company up for success by ensuring you’re prioritizing data privacy.
EPISODE 004 – Thinking Bigger About Disaster Recovery Plans, and Preparing for and Responding to Breaches
Why some disaster recovery plans are failing during COVID-19 and how organizations should prepare and respond to breaches more holistically.
EPISODE 003 – How One Clinic is Leveraging Telemedicine and Technology to Manage Through COVID-19
Hear from a Chief Medical Officer about how his clinic in Boston is managing COVID-19 challenges with telemedicine and technology solutions.

EPISODE 002 – Developing the Cyber Security Governance of a Nation – A Mix of IT and Strategic Planning
Behind the scenes with a former CIA CISO, developing the role of a CISO within the CIA, U.S. History and the Civil War, cooking, traveling, and cats.
EPISODE 001 – Cyber Security Education and the Ethics of Teaching Students to Break Things
Cyber security education, iOS vs. Android, Wall of Sheep initiative at DefCon, and Fifa.